Software Development
14 minutes reading time

SDLC, or the Software Development Life Cycle, is a structured process for planning, building, testing, deploying, and maintaining software applications. It works by dividing software development into defined phases, with clear activities and deliverables at each stage. Teams use it to meet project needs, manage risks, maintain code standards, and improve software quality.
In this guide, we'll go deeper into the SDLC meaning, how the process works, and how to apply it in practice. We’ll discuss:
Let’s get right to it!
The SDLC process gives each phase a clear purpose, set of activities, and expected output. Teams can move through these phases sequentially, iteratively, or continuously, depending on the model they choose. This structure creates shared checkpoints for reviewing requirements, quality, risk, and release readiness.
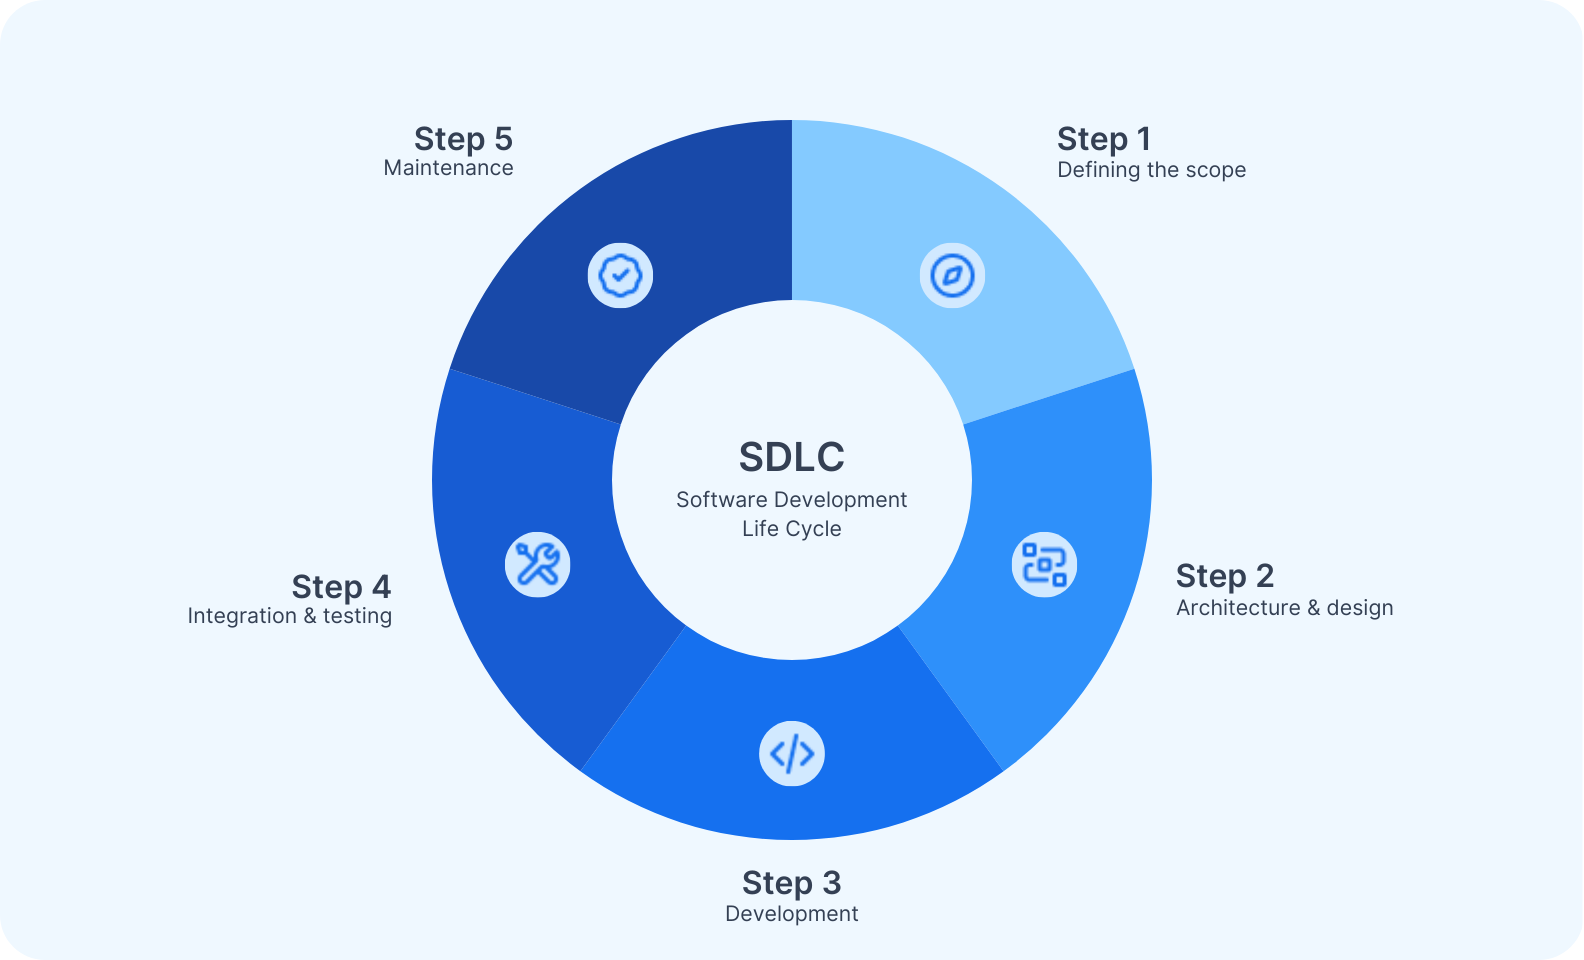
Following this process helps the software meet customer expectations and project requirements, which is why each phase matters.
A defined SDLC gives teams shared checkpoints for planning, quality, cost, risk, and customer feedback. The five benefits below show where that structure helps.
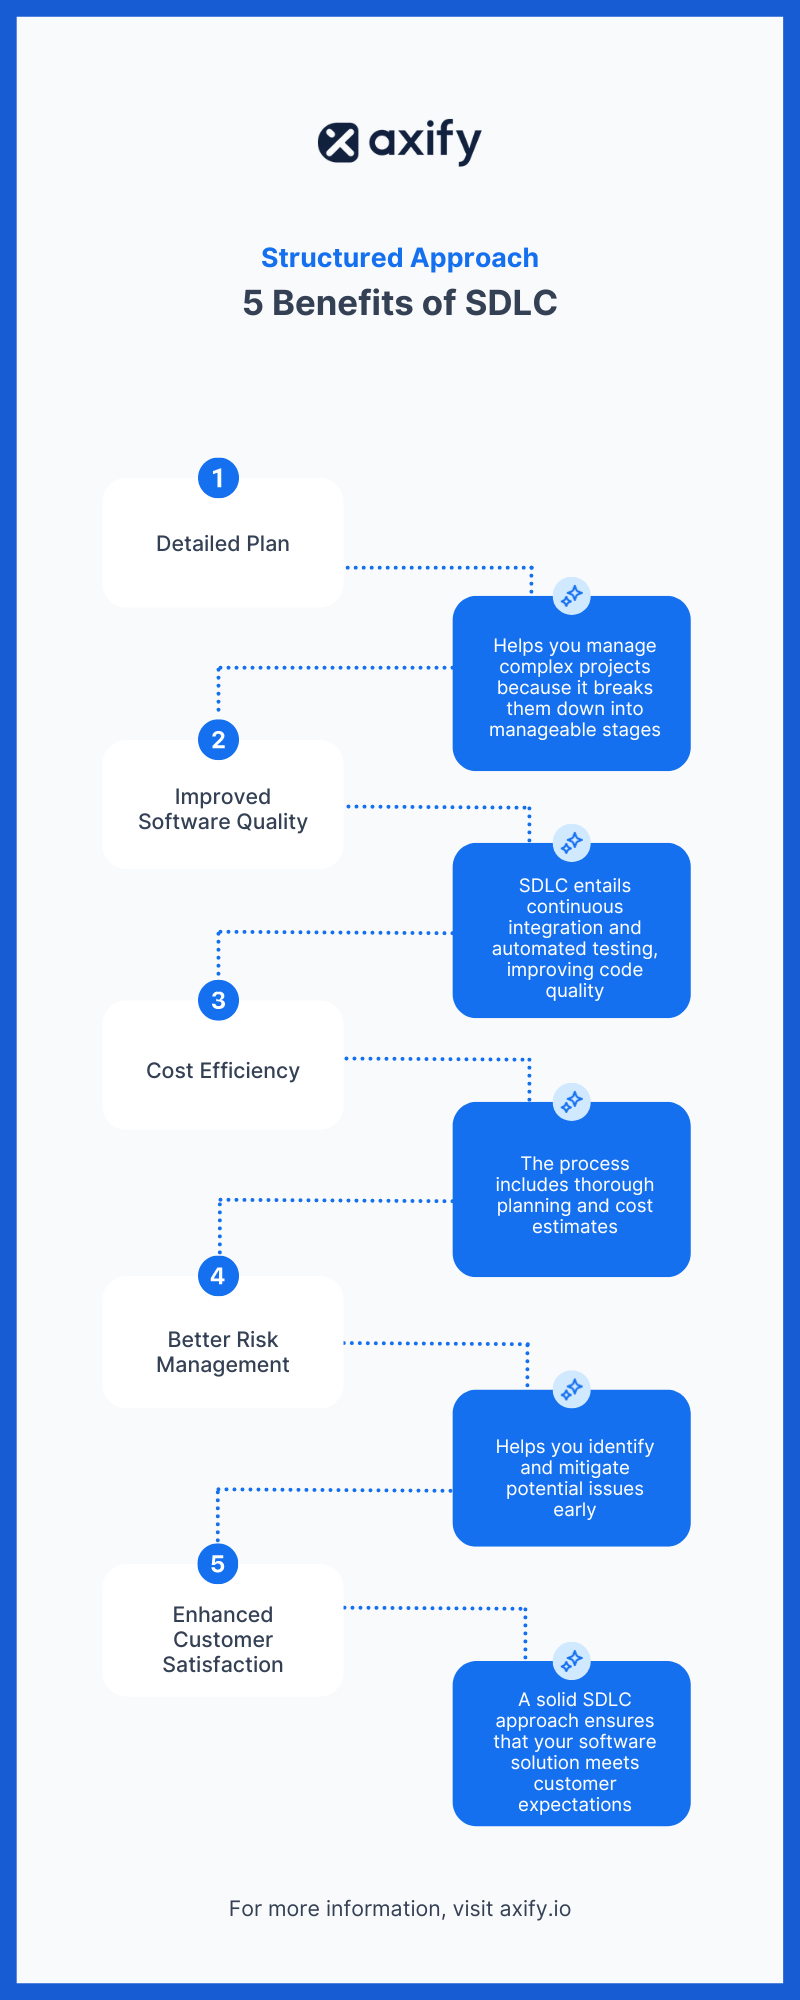
SDLC means having a detailed plan for your development process. This structured approach helps you manage complex projects because it breaks them down into manageable stages.
That’s how you reduce potential risks and ensure each phase is completed thoroughly.
Insider Tip: In our company, our teams have ownership and responsibility from development to deployment. We recommend that you involve stakeholders from development, testing, and project management to decide the next features to prioritize. Regularly seek their feedback on what you built and their insights on market and customer needs. This approach is great for quality assurance because you get continuous feedback on which you can base your improvements. More importantly, it prevents costly rework.
As we said above, the SDLC gives teams defined quality checks throughout development. Depending on the model, these checks may include design reviews, code reviews, automated tests, integration tests, and acceptance testing. Applying them throughout the lifecycle helps teams find defects earlier and verify that the software meets its requirements.
Insider Tip: With test-driven development, developers write a failing unit test before the corresponding production code. They then add enough code to pass the test and refactor the result. This short feedback loop can improve test coverage and make defects easier to catch during development.
An SDLC approach can help teams control project costs by clarifying scope, dependencies, resources, and risks before development expands. Early estimates also create a baseline for tracking budget changes as requirements evolve.
Insider Tip: Apply shift-left testing by introducing automated checks, code reviews, and security testing earlier in development. Finding defects before integration or release reduces the time and cost required for rework later in the SDLC.
SDLC makes risk reviews part of delivery planning, although their timing depends on the chosen model. Teams can identify technical, security, schedule, and resource risks early and review them again as the project changes.
Insider Tip: Adapt risk reviews to your SDLC model. The Spiral model evaluates risk during every iteration, while the V-model uses formal verification and validation activities before work advances. Meanwhile, Agile teams review risks continuously during planning, development, testing, and retrospectives.
Regular validation throughout the SDLC helps teams keep the product aligned with customer needs. Early feedback also gives them time to correct gaps before release.
Insider Tip: Regularly involve customers in the review process, especially during the planning and testing phases. Use feedback loops to make iterative improvements based on their input.
We’ve been explaining that SDLC consists of different phases. In this section, we’ll explain what each phase entails and how to conduct it step by step.
Side note: Different sources cite varying numbers of SDLC phases, ranging from five to eight. Some stop at deployment, while others include operation and monitoring. The key is to adapt this plan to fit your team’s unique needs and workflows and to support your project requirements.
| Phase | Purpose | Deliverable |
|---|---|---|
| Planning | Define scope and goals | SRS document |
| Analysis | Refine requirements | Detailed specifications |
| Design | Define product architecture | SDD document |
| Development | Build the software | Functional source code |
| Testing | Verify quality and requirements | Test report |
| Deployment | Release the software | Production release |
| Maintenance | Support and improve the software | Updates and maintenance records |
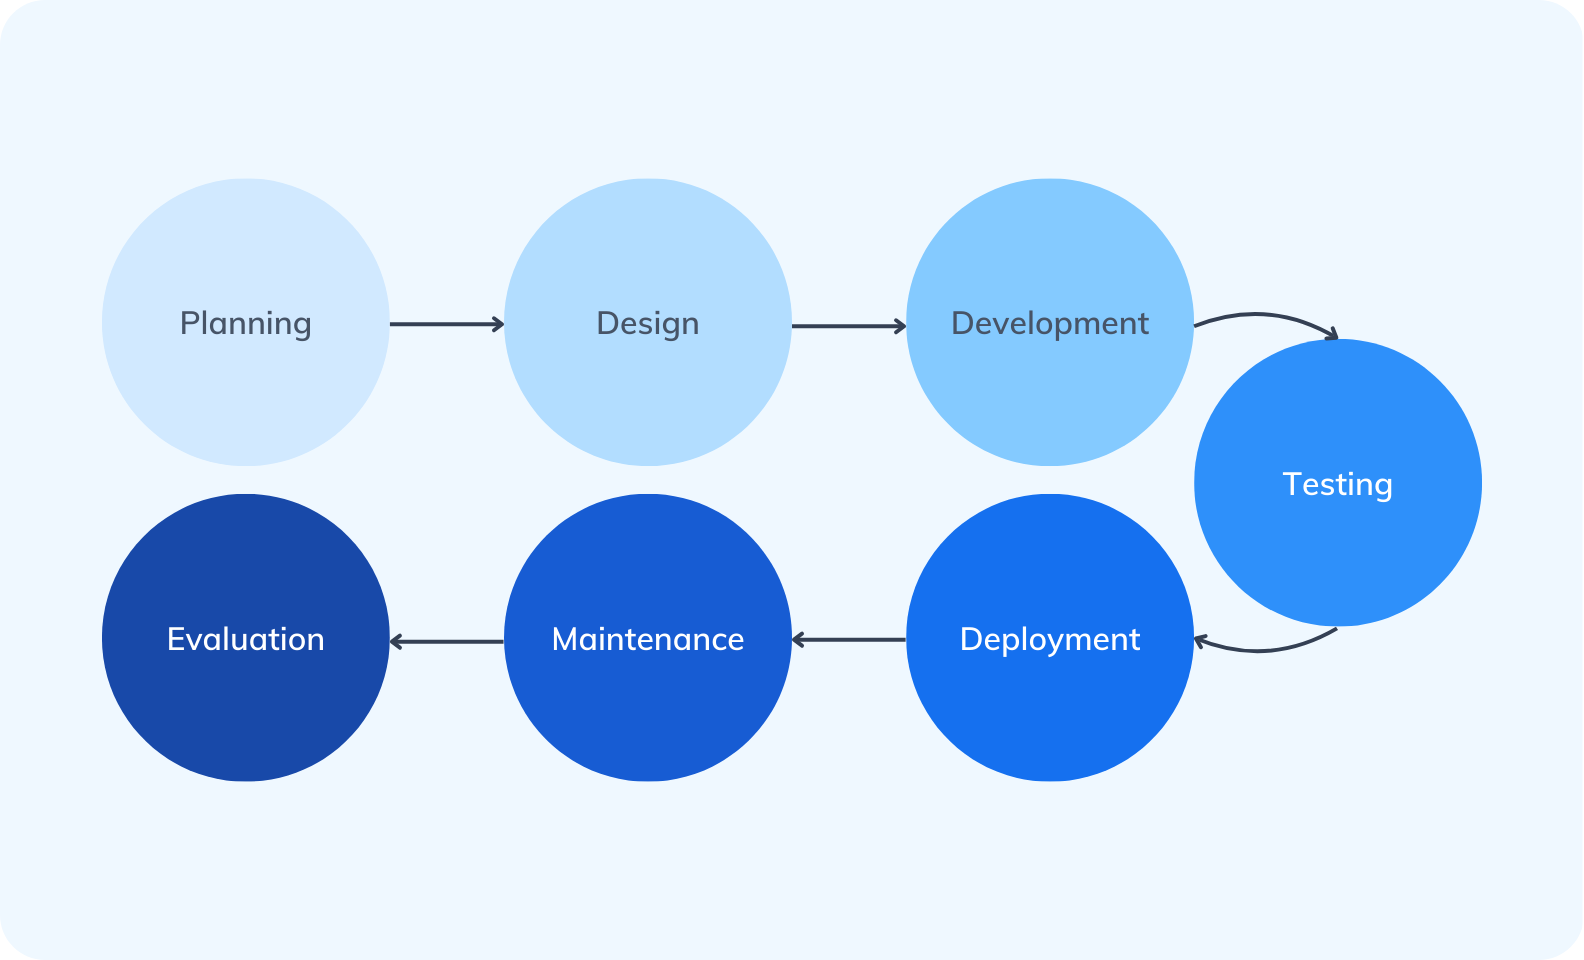
The planning phase is the foundation of the Software Development Life Cycle approach. This is where you define the project requirements, scope, and objectives. Plus, you’ll be gathering business requirements, understanding the customer’s needs, and setting clear goals. This phase also includes initial cost estimates, time frames, and risk analysis.
How to conduct it step-by-step:
Insider Tip: Use collaborative tools like Microsoft Teams, Slack, and Trello to involve all stakeholders in the planning stage. That’s how you reduce potential issues later.
The analysis phase of SDLC turns the initial project requirements into detailed specifications that developers and designers can use. During this phase, the team clarifies what the software must do, identifies constraints, and resolves gaps before design begins.
How to conduct it step-by-step:
Insider Tip: Keep requirements specific and testable. A requirement such as “the page should load within two seconds” gives development and testing teams a clearer target than “the page should load quickly.”
The design phase involves creating your software system’s architecture. In this phase, you’ll translate the detailed requirements from the analysis phase into a blueprint for constructing the software.
How to conduct it step-by-step:
Insider Tip: Involve both software developers and end users in design reviews. Developers can provide insights into technical feasibility, while end-users can ensure the design meets their needs and expectations. This collaborative approach leads to a more user-friendly design.
The development phase is where the actual coding of the software takes place. In this phase, you transform the design specifications into functional software. This phase requires careful management because you want your code to be developed efficiently and meet the design requirements.
How to conduct it step-by-step:
Insider Tip: Encourage pair programming, where two developers work together on the same code. One developer writes the code while the other reviews it in real time. This can improve code quality and spread knowledge across the team.
During the testing phase, your team will check that the software meets all specified requirements. Plus, they can sleuth out any defects or issues. This phase ensures the quality and reliability of your software before it’s deployed to users.
How to conduct it step-by-step:
Insider Tip: Implement automated testing tools such as Selenium, JUnit, and TestNG to streamline repetitive tests and catch defects early. Automated tests can run continuously and provide quick feedback, speeding the testing process significantly.
The deployment phase involves releasing the software to the production environment where it will be accessible to end users. This phase includes all activities necessary to make the software operational.
How to conduct it step-by-step:
Insider Tip: Conduct a pilot deployment with a small user group before a full-scale release. This approach allows you to identify and resolve any issues in a controlled environment, reducing the risk of widespread problems during the full deployment.
The Maintenance Phase involves ongoing support and updates for the software. Your team will have to ensure the software continues to function correctly and remains relevant. This phase also includes reviewing results and documenting lessons that can improve future projects.
How to conduct it step-by-step:
Insider Tip: Set up a dedicated maintenance team responsible for monitoring and updating the software. This team should work closely with support staff and maintain a shared repository for lessons learned, project documentation, and practices that can improve future projects.
So, now you know how the SDLC approach works in principle. However, there are different models you can use.
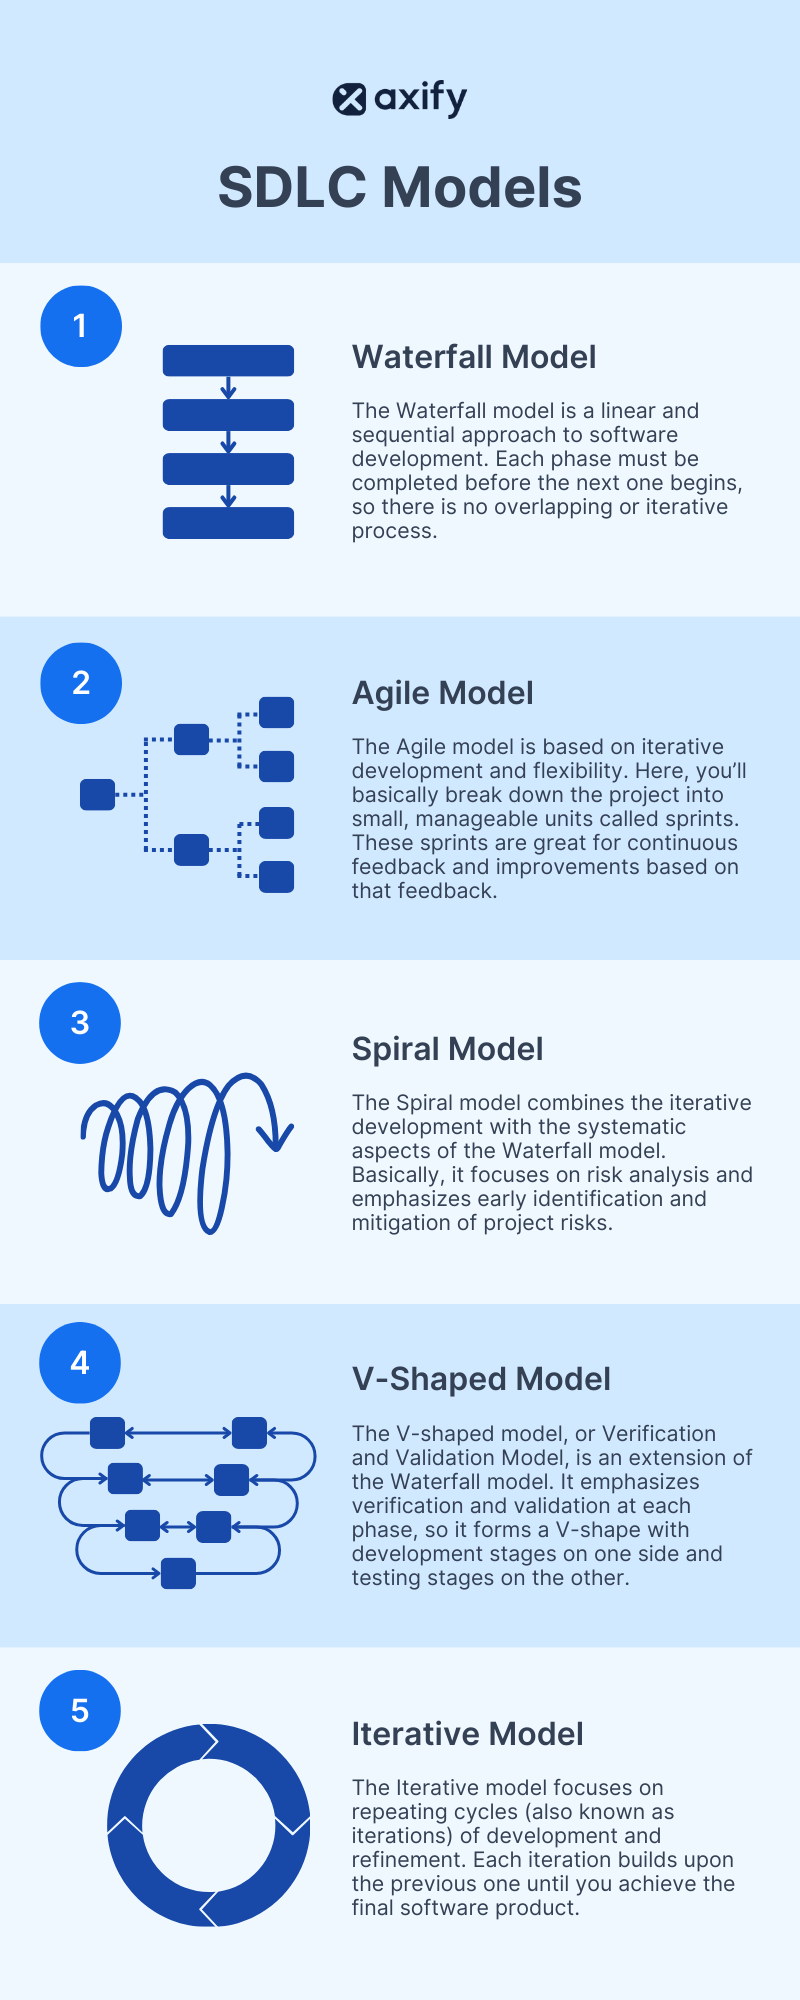
The Waterfall model is a linear and sequential approach to software development. Each phase must be completed before the next one begins, so there is no overlapping or iterative process.
Best for: Fixed-scope, well-documented projects with stable requirements.
Pros:
Cons:
The Agile model is based on iterative development and flexibility. Agile teams deliver work in small increments through iterative or continuous workflows. Scrum teams organize that work into fixed-length cycles called sprints. These sprints are great for continuous feedback, and improvements based on that feedback.
Best for: Projects with changing requirements that benefit from frequent delivery and customer feedback.
Pros:
Cons:
Rapid Application Development, or RAD, prioritizes fast prototyping, frequent user feedback, and repeated improvements. Instead of completing every SDLC stage in a strict sequence, teams build working prototypes and refine them through short development cycles.
RAD can help modern software engineering teams reduce cycle time when requirements are expected to evolve. However, it depends on regular user involvement and a team that can make design and development decisions quickly.
Best for: Time-sensitive projects that can be divided into software modules and refined through frequent user feedback.
Pros:
Cons:
The Spiral model combines the iterative development with the systematic aspects of the Waterfall model. Basically, it focuses on risk analysis and emphasizes early identification and mitigation of project risks.
Best for: Large, complex, or high-risk projects that require repeated risk analysis.
Pros:
Cons:
The V-shaped model, or Verification and Validation Model, is an extension of the Waterfall model. It emphasizes verification and validation at each phase, so it forms a V-shape with development stages on one side and testing stages on the other.
Best for: Regulated or safety-critical projects with stable requirements and formal testing standards.
Pros:
Cons:
The Iterative model focuses on repeating cycles (also known as iterations) of development and refinement. Each iteration builds upon the previous one until you achieve the final software product.
Best for: Projects where teams understand the main goal but expect requirements to become clearer during development.
Pros:
Cons:
The Big Bang model uses little formal planning or standard work. Development begins with the available requirements and resources, while the final direction may emerge as the project progresses.
Best for: Very small experiments, prototypes, or solo projects with limited scope and low financial risk.
Pros:
Cons:
SDLC is great, but it’s not the only lifecycle management methodology. Let’s see how it stacks up against other options.
SDLC defines the stages a software product moves through from planning to maintenance. Agile is an iterative model for organizing those stages, with teams revisiting planning, development, and testing during short delivery cycles.
As such, SDLC:
Agile:
SDLC defines the activities and deliverables across a software product’s lifecycle. DevOps connects development and operations through shared ownership, automation, and continuous feedback.
SDLC:
DevOps:
SDLC and Lean methodology have different focuses. SDLC is a detailed and structured approach to software development, while Lean focuses on optimizing efficiency and minimizing waste. Lean thinking is also behind value stream management, which tracks how work flows through the whole lifecycle.
SDLC:
Lean:
SDLC defines the stages used to plan, build, test, deploy, and maintain software. DevSecOps adds continuous security practices to those stages and gives development, security, and operations teams shared responsibility for protecting the software.
A secure SDLC follows the same principle by building security requirements, reviews, and testing into the development process. This approach helps teams identify vulnerabilities while changes are easier and less expensive to address.
Shift-left security means moving security work earlier in the SDLC instead of waiting for a final security review before deployment. Security activities can map to each phase in the following ways:
DevSecOps also uses automation to run these checks throughout development. This makes security findings visible sooner and gives teams more time to fix them before software reaches production.
SDLC can refer to the Software Development Life Cycle or the Systems Development Life Cycle. The software definition focuses on creating and maintaining software applications, including planning, design, coding, testing, deployment, and maintenance.
The Systems Development Life Cycle has a broader scope. It can cover software, hardware, infrastructure, data, business processes, and the people who operate the complete system. For example, introducing a new payment platform may require application development, server configuration, data migration, employee training, and changes to internal procedures.
Both definitions use structured phases to manage requirements, implementation, testing, and ongoing support. The correct meaning depends on the project scope. A software product usually follows the Software Development Life Cycle, while a wider technology or business system may require the Systems Development Life Cycle.
SDLC manages the stages involved in developing and maintaining software. Meanwhile, Six Sigma uses data and statistical analysis to reduce defects and process variation.
Software engineering teams may use Six Sigma techniques to examine recurring quality problems. But it does not replace the planning, design, development, testing, deployment, and maintenance stages of SDLC.
SDLC guides the creation and maintenance of software, while ITIL provides practices for managing the digital products and services that surround it. Current ITIL terminology includes incident management, change enablement, release management, and continual improvement.
Teams may use SDLC to develop an application and ITIL practices to manage the supporting service throughout operation and improvement.
AI and automation can support specific SDLC activities, but their impact depends on how teams integrate and govern the tools. AI may help analyze requirements, generate code, create test cases, and summarize production signals. Automation can handle repeatable build, testing, and deployment work.
The outcome still depends on review quality, feedback speed, and workflow constraints. DORA’s 2024 report found that a 25% increase in generative AI adoption was associated with a 1.5% decrease in delivery throughput and a 7.2% decrease in delivery stability. This finding shows why teams should measure AI across the full delivery system.
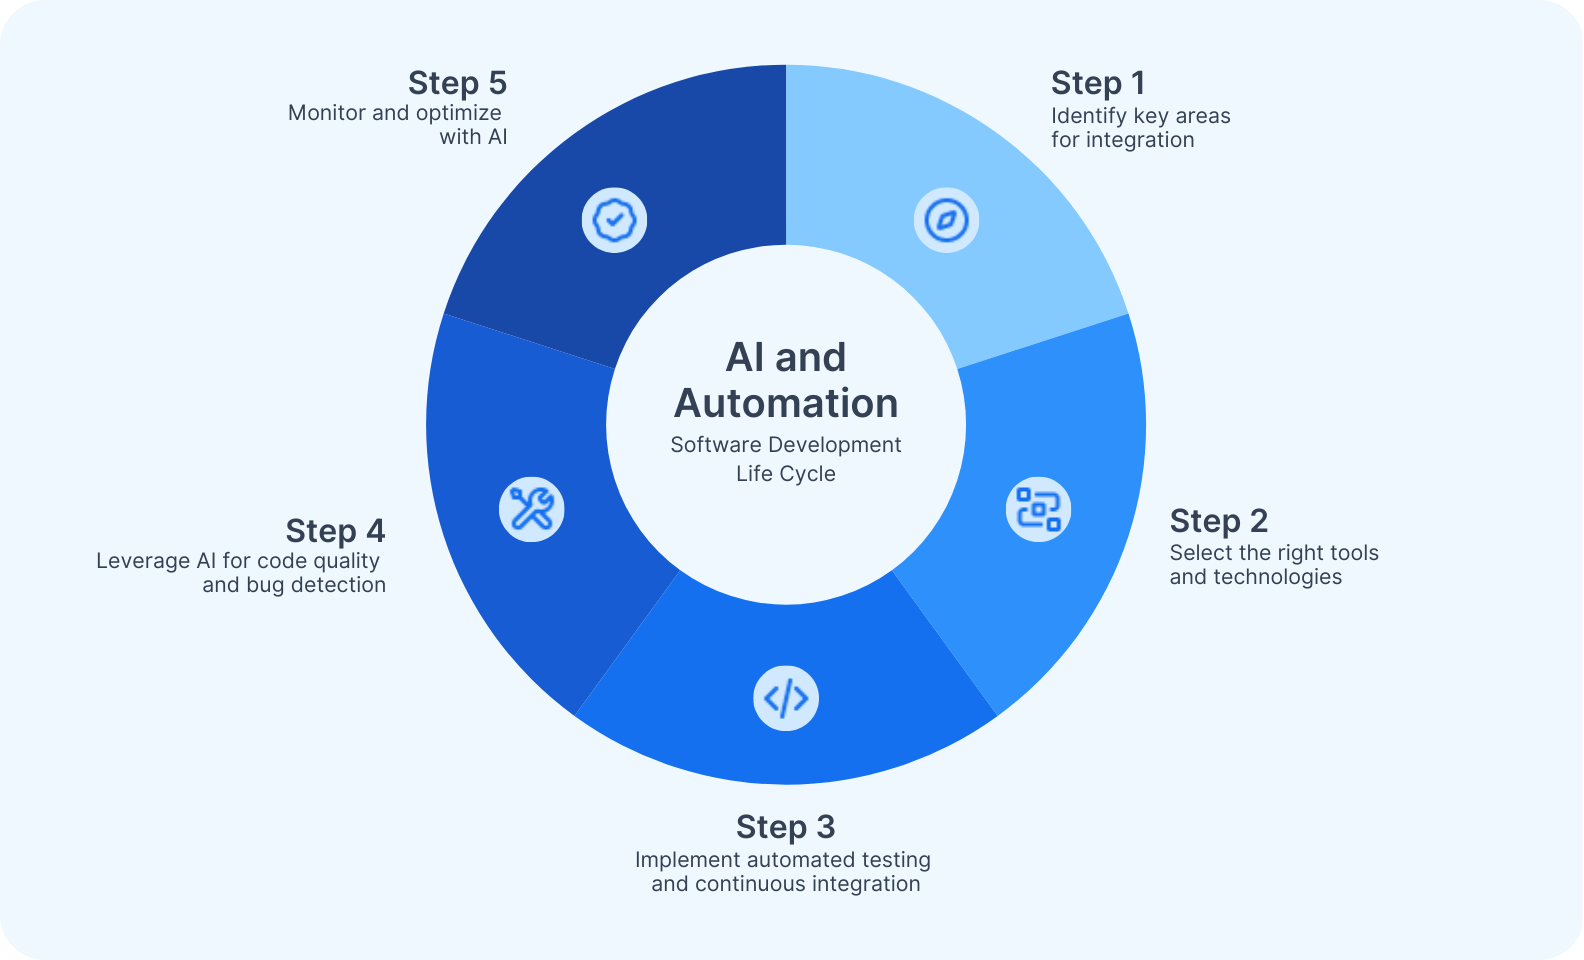
An AI-enabled SDLC applies AI tools and automation to specific activities across the development lifecycle. Each of them should support a defined task, and your team should review the output before it affects the product or production environment.
Here are the main ways AI and automation can support each SDLC phase:
The right SDLC software supports a specific part of your workflow rather than trying to manage every activity through one platform. These are the tools you should use.
Insider Tip: Train your team on the latest AI and automation tools continuously. This constant learning and adaptation will help you maximize the benefits of AI and automation in your development process. You can even set up a dedicated task force to oversee AI and automation initiatives to make sure they’re integrated well and regularly optimized.
Axify connects engineering data from your delivery tools and AI coding assistants, then turns it into metrics, comparisons, and recommendations you can use across the SDLC. Its current capabilities focus on AI adoption, delivery impact, AI costs, and the workflow constraints that affect how quickly work reaches production.
Here’s how Axify supports those decisions:
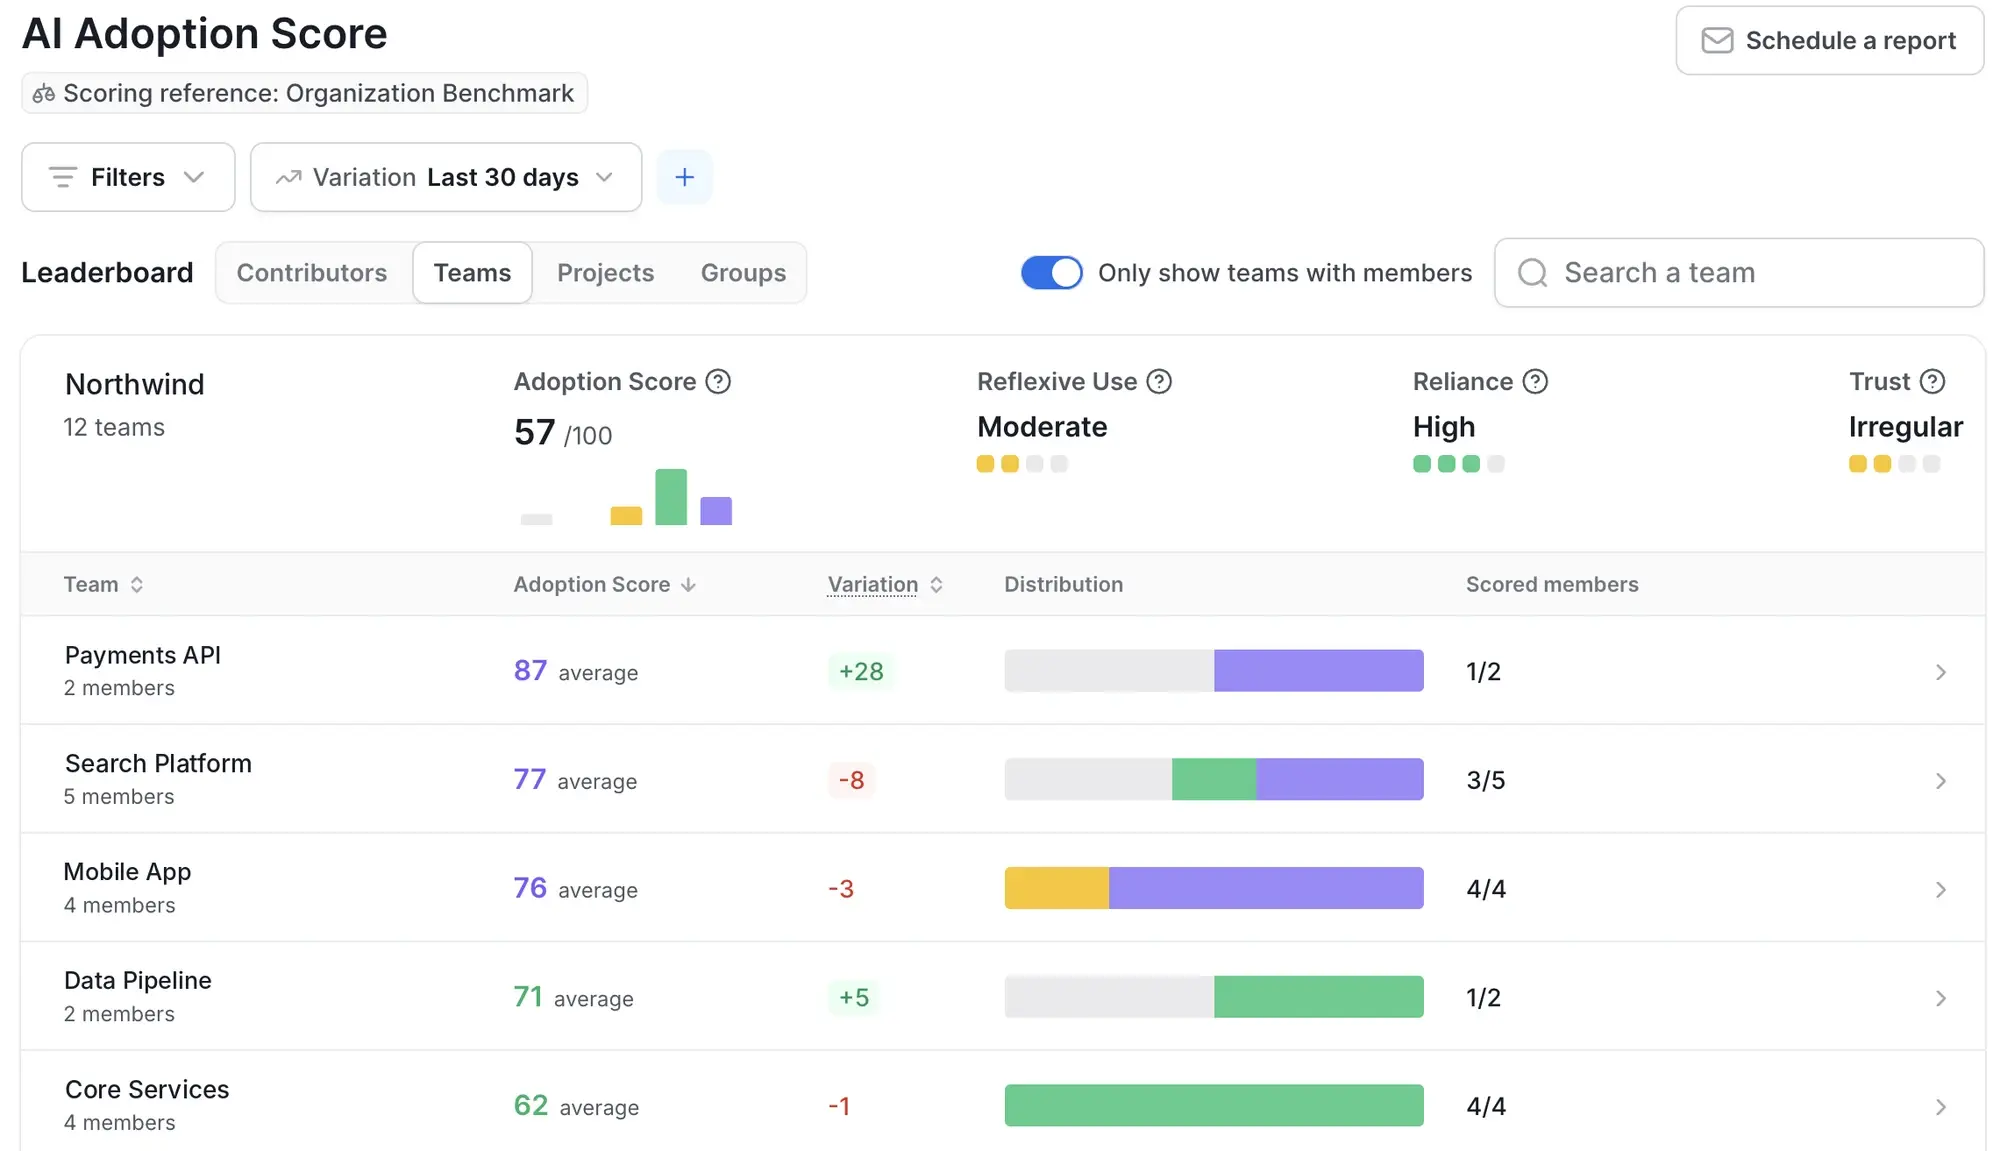
Axify's AI Adoption feature puts into perspective the use of AI tools such as GitHub Copilot, Cursor, and Claude Code. You can review active users, licensed users, usage frequency, and acceptance rate by team, project, or line of business, along with an AI adoption score built on three pillars: reflexive use, reliance, and trust. Our guide to AI adoption explains what to look for.
This separates purchased licenses from active adoption. For example, a team may have access to an AI assistant while accepting few of its suggestions. Axify makes that gap visible so you can decide where training, tool changes, or closer review may be useful.
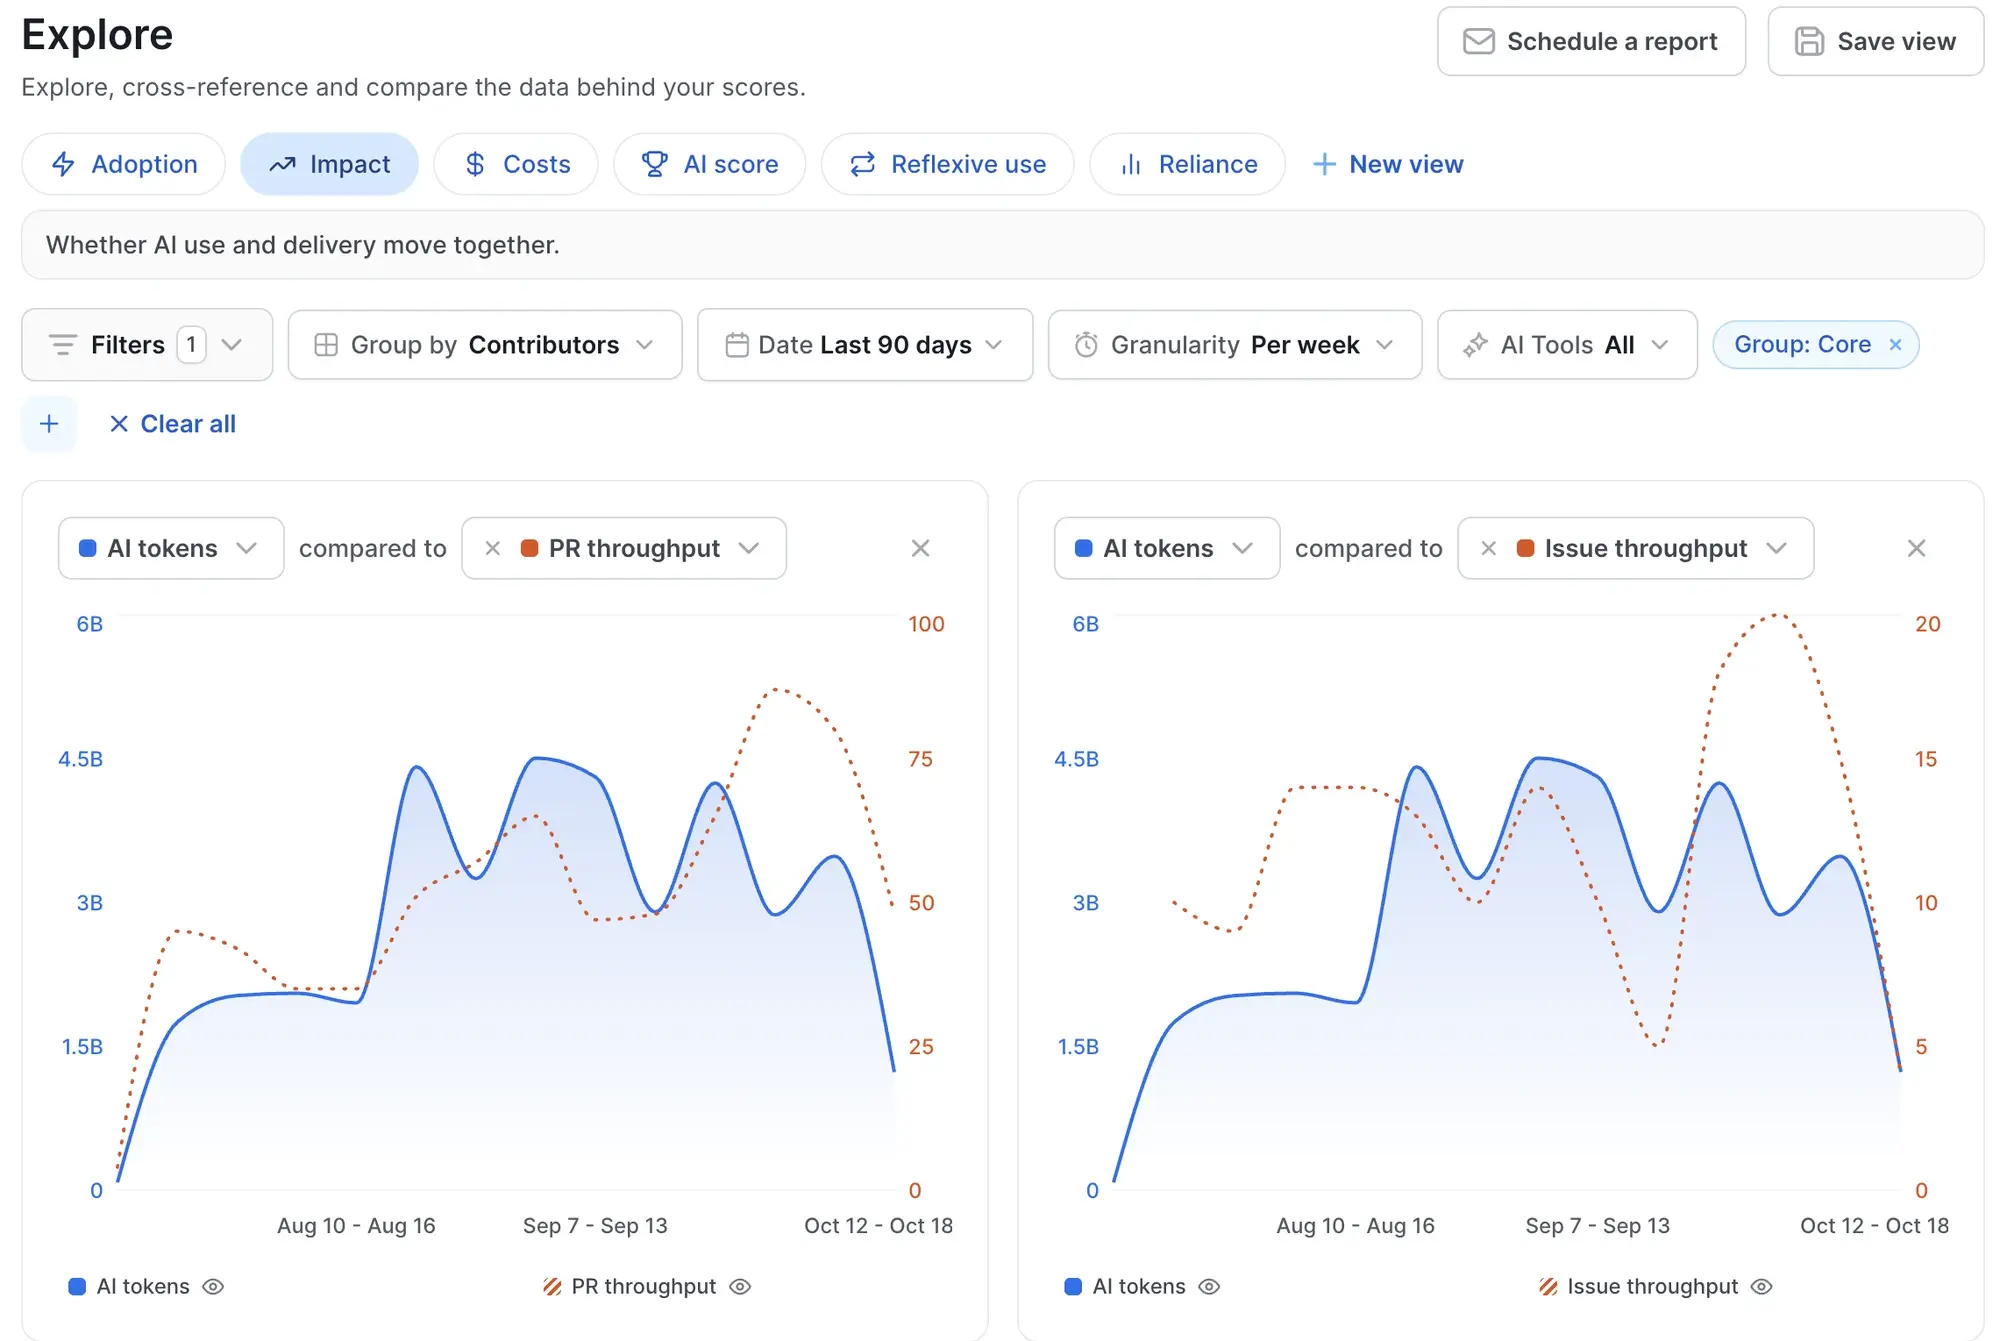
Faster code generation does not automatically mean faster software delivery. Axify compares engineering metrics such as cycle time, throughput, review time, and DORA metrics before and after AI adoption.
Reviewing these signals over the same period helps you see whether higher AI adoption is followed by shorter delivery times or by new delays in testing and code review.
This comparison works at the team, project, or business-line level because delivery results depend on shared workflows, dependencies, and review policies rather than one developer’s output alone.
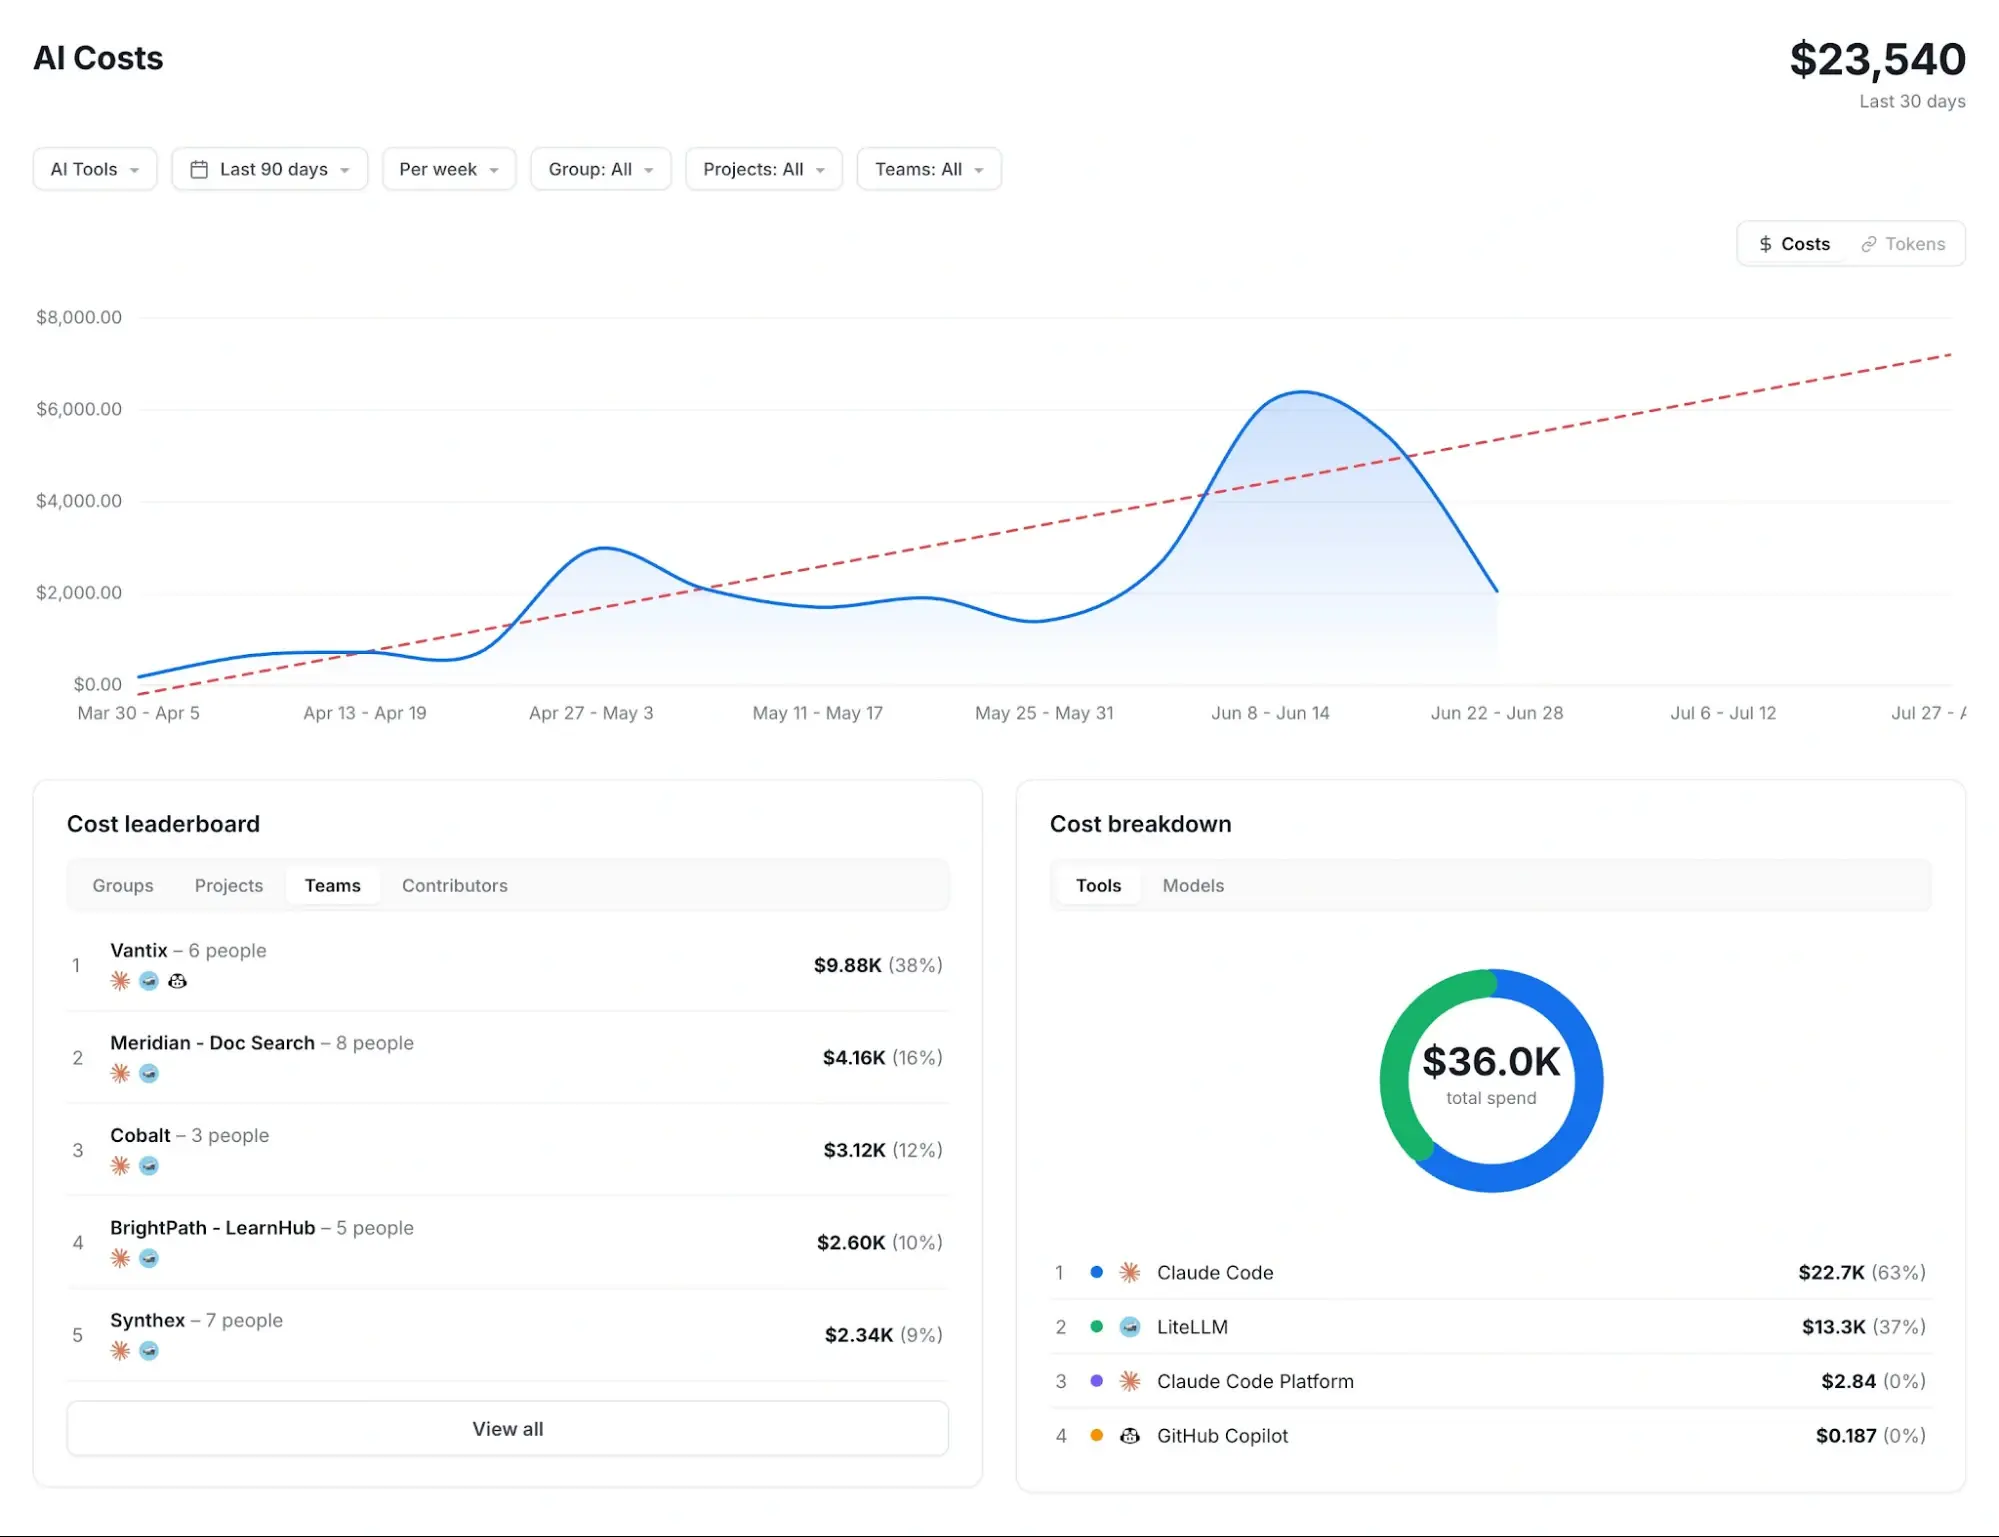
Axify gives you a centralized view of AI spending alongside adoption and delivery data. The cost dashboards show total spend over time and break it down by AI tool, model, project, team, or contributor.
For example, you can compare Claude Code, GitHub Copilot, or specific Claude models to see which ones account for the largest share of spending. From there, you can review whether the teams using those tools are also showing stronger adoption or improved delivery metrics during the same period.
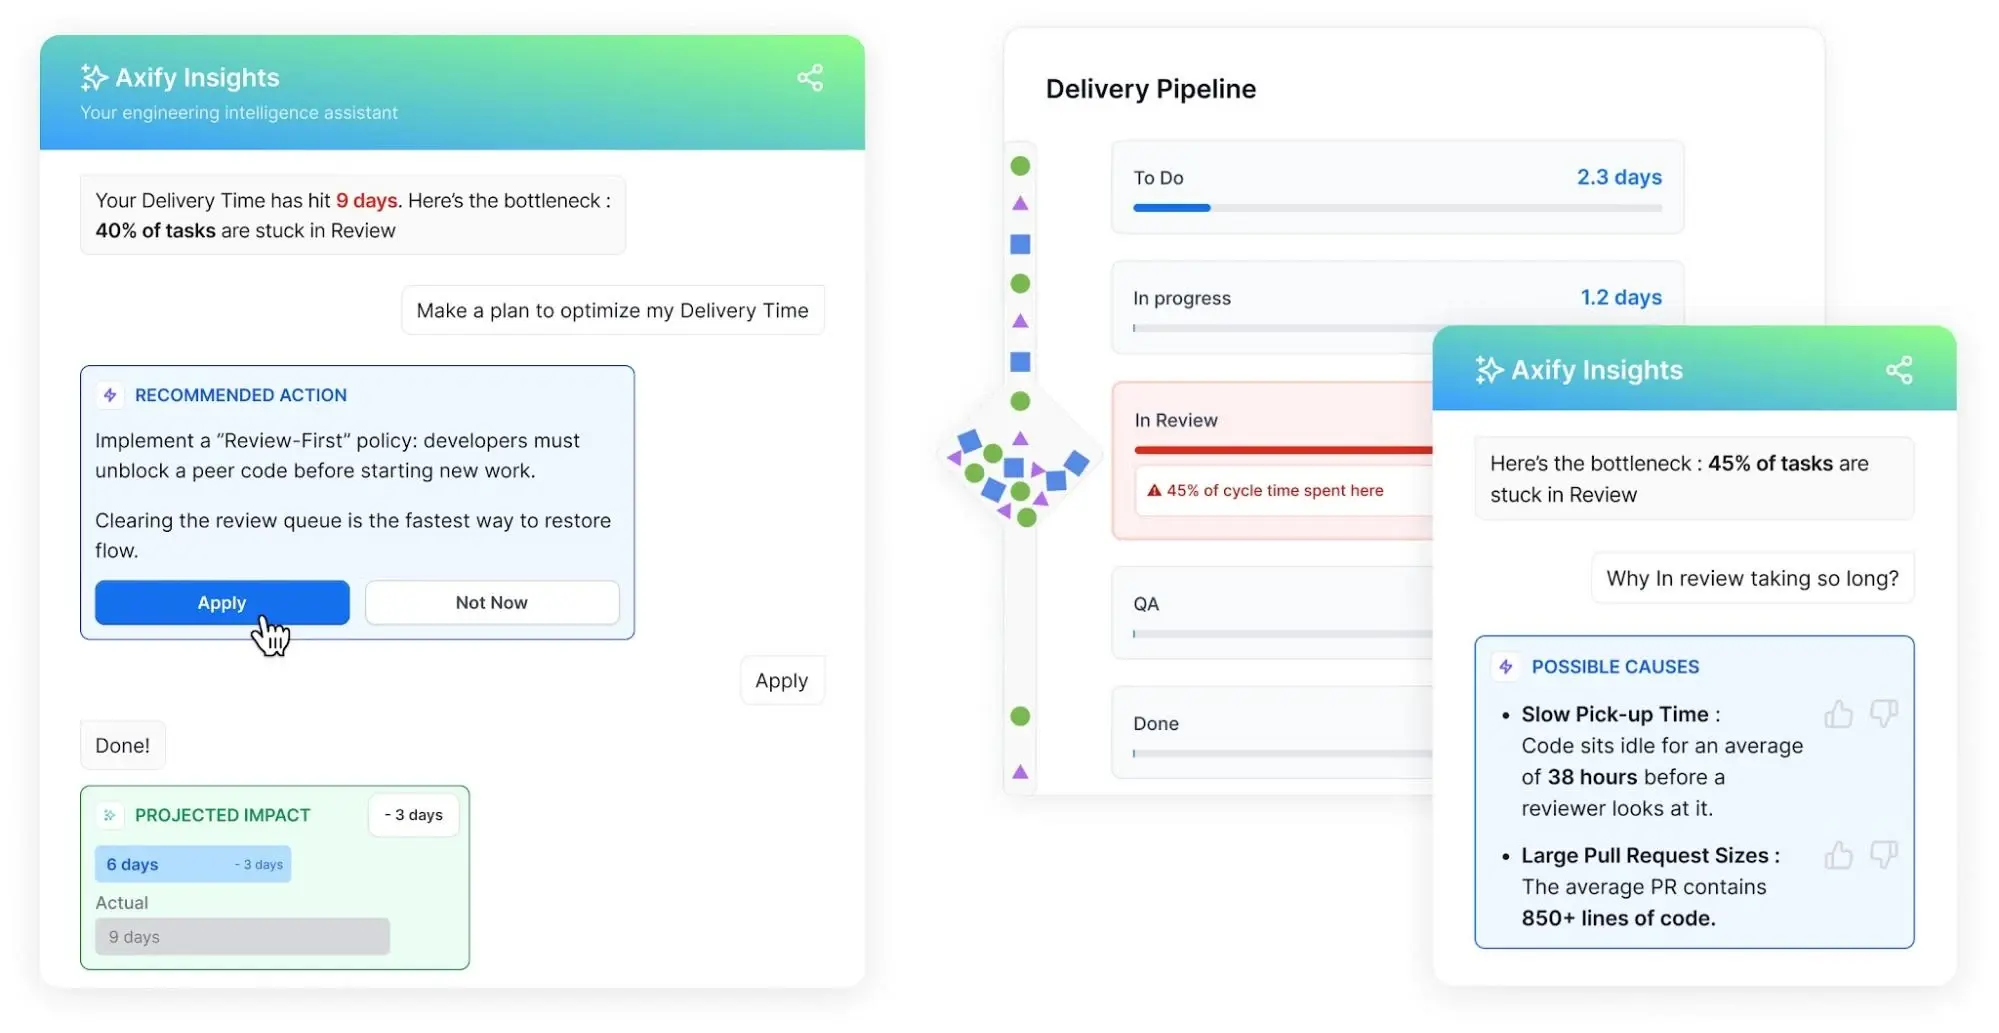
Axify Intelligence analyzes delivery data to identify where work is slowing down and which conditions may be contributing to the change. It can surface patterns such as long review queues, growing work in progress, slow pull request pickup, or large pull requests.
The feature also suggests actions tied to the detected constraint. For example, if review time increases because work is waiting for an available reviewer, Axify Intelligence may recommend changing review ownership or limiting parallel work.
These recommendations support your investigation, while your team decides whether the suggested action fits its actual workflow.
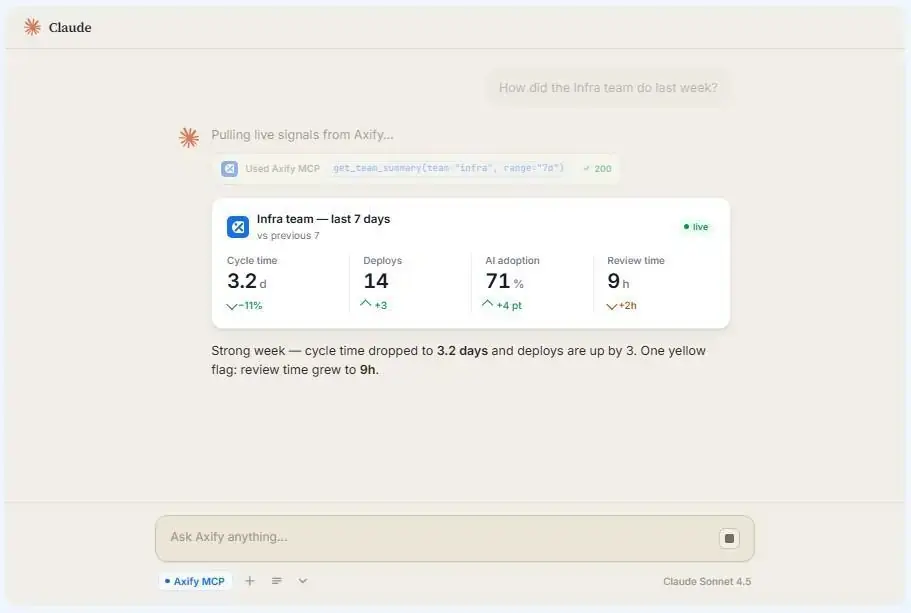
Axify MCP connects live Axify data to MCP-compatible AI clients. This allows engineering leaders to ask questions about DORA metrics, cycle time, delivery signals, and AI adoption from tools such as Claude, ChatGPT (Business, Enterprise, and Edu), Cursor, or any MCP client that supports OAuth.
The connection uses OAuth and follows the access permissions already configured in Axify. Queries are permission-scoped, logged, and read-only.
This gives you another way to review live engineering data and combine several metrics in one question without manually assembling separate dashboard reports.
The real test of an SDLC is not whether every team follows the same seven phases. It is how quickly the organization turns uncertainty into verified production learning without shifting risk into review, testing, or operations.
AI makes that distinction more important.
As code becomes easier to produce, unclear requirements, weak validation, and limited review capacity become more expensive. A mature SDLC applies controls according to risk: routine changes move quickly, high-risk changes receive deeper scrutiny, and teams can trace each decision when results differ from expectations.
Engineering leaders should therefore evaluate the SDLC by its decision latency.
How long does it take to recognize a flawed requirement, identify a delivery constraint, validate a release, and change direction? Improving those feedback loops matters more than enforcing a theoretically perfect process.
To examine how AI changes those feedback loops across planning, development, testing, review, and production, read Axify’s guide on how AI is reshaping the software development lifecycle.
Axify shows where work waits across your SDLC, how AI adoption and AI costs evolve by team, and how your delivery metrics respond, so you can shorten those feedback loops with data.
Want to see your own delivery and AI data in one place? Start your 14-day free trial of Axify.

No. Teams can use different workflows when their products, risks, and release patterns differ. Standardize the controls that protect the organization, such as security and production-readiness criteria, while allowing teams to adapt planning, review, and deployment practices to their delivery context.
Review how much time work spends waiting for approvals and whether those controls reduce failures or rework. If approval queues grow without improving outcomes, narrow the control to higher-risk changes instead of applying the same review depth to every release.
Usually, review at least two or three comparable delivery cycles before deciding whether the change worked. Low-frequency release environments may require a full quarter. Keep the work type and reporting boundaries consistent so differences in scope do not distort the result.
Usually not. AI-assisted work should meet the same quality, security, and production-readiness standards as human-written work. However, teams may need additional evidence, such as code provenance, stronger automated checks, or documented human review, depending on the change’s risk.
Escalate findings that affect commitments, investment, or organizational risk: persistent cross-team constraints, unstable releases, growing rework, delayed strategic initiatives, and AI costs without delivery improvement. Executives need the decision and its evidence.